
/SETUP GUIDES
Overview
What the PrivateLink connection does, who builds which part, and what each side hands over.
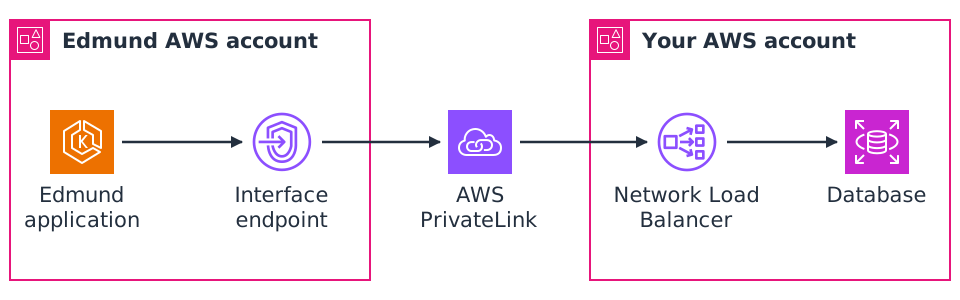
Edmund reads a database in the customer’s AWS account through AWS PrivateLink. The customer publishes one database port as an endpoint service. Edmund connects to it from its own AWS network.
Traffic stays inside AWS. The two networks are never joined, so their address ranges may overlap. Edmund reaches only the published port, and connections can be opened only from Edmund’s side.
For a database outside AWS, use the Site-to-Site VPN.
Scope of this document
| Part | Covers | Done |
|---|---|---|
| Overview | Responsibilities, the exchange between the two sides, security | — |
| Setup | Load balancer, endpoint service, database user, accepting the connection — with example values and commands | Once, by the customer’s AWS administrators |
Division of responsibility
| Task | Customer | Edmund |
|---|---|---|
| Send the AWS account ID and region | ● | |
| Build the load balancer in front of the database | ● | |
| Create the endpoint service and allow Edmund’s account | ● | |
| Create a read-only database user | ● | |
| Create the interface endpoint | ● | |
| Accept the connection request | ● | |
| Configure the connection and test it | ● | |
| Keep the load balancer target current after a database failover | ● |
The exchange
| Step | Edmund | Customer |
|---|---|---|
| 1 | Provides its AWS account ID and region; for the Shared Cloud Deployment (SaaS) they are listed in Setup. If the database is in a different region, the connection is cross-Region and Setup lists the extra requirements | Builds the endpoint service, then sends the service name and the database details |
| 2 | Creates the interface endpoint, which sends a connection request | Accepts the connection request |
| 3 | Tests the connection: login, schema, test query | — |
Security summary
| Concern | How it is addressed |
|---|---|
| Public internet | Not used; traffic stays inside AWS |
| Who can connect | Only Edmund’s AWS account, after the customer accepts the connection |
| What Edmund can reach | Only the port behind the customer’s load balancer |
| Access to Edmund’s systems | None; connections are opened only from Edmund’s side |
| Revoking access | The customer rejects the endpoint connection; see Setup |
Terms
| Term | Meaning |
|---|---|
| Endpoint service | The customer’s database port, published through PrivateLink |
| Service name | The identifier of the endpoint service, com.amazonaws.vpce.<region>.vpce-svc-…. Edmund needs it to connect |
| Allowed principal | An AWS account permitted to request a connection. Only Edmund’s account is listed |
| Interface endpoint | Edmund’s side of the connection, inside Edmund’s network |
| Network Load Balancer | The customer’s internal load balancer that forwards the connection to the database |